About Us
Red team operations, social engineering, and physical security auditing.
In a pivotal moment of The Matrix movie, Neo is spellbound by a striking woman in a red dress moving gracefully through a simulation.
The real danger wasn't in the red dress or the allure, but in the distraction itself. That red dress wasn’t just a flourish of code, it was a tool, a device, a psychological exploit crafted to misdirect and disarm. And in that split second of wonder, the danger was already upon him.
What draws your attention can be precisely what blinds you to the attack, and in the hands of a skilled adversary, distraction becomes a weapon.
This is the essence of social engineering - not brute force, but subtle subversion. Not breaking through walls, but walking through doors left open by trust, assumption, and inattention.
The Woman in Red doesn’t need to be a threat to become one, she simply needs you to believe that she isn't.
Who We Are
We specialize in unmasking vulnerabilities through the eyes of an adversary. Woman in Red provides specialized Social Engineering assessments and Physical Security audits designed to test the human element of security.
Our approach is ethical, authorized, and deeply rooted in the psychology of security. We help organizations strengthen their defenses not by just building higher walls, but by understanding how easily doors can be opened.
Our name comes from a famous scene in The Matrix, where a woman in a red dress draws Neo's attention just long enough for the real threat to appear. It is a reminder of what we do every day: attackers rarely force their way in. They distract, persuade and blend in. From phishing and cold calls to covert building entry and long-term adversary simulation, we show you how that happens in your organization, and how to stop it.
Our Approach
Authorized & Ethical, Always
Every engagement is carried out under explicit, written client authorization, with clear rules of engagement and agreed boundaries. We do not support or perform malicious activity of any kind.
The Adversary's Perspective
We think and act like real attackers, combining technical, physical and human attack paths, because real threats don't stay within a single category.
People First, No Blame
When we test your staff, the goal is to strengthen your security culture, never to shame individuals. Findings are handled with discretion and every mistake becomes a lesson.
Clear, Actionable Results
Our reports speak to both technical teams and leadership, with evidence for every finding and practical fixes prioritized by risk and cost.
Meet the Founder
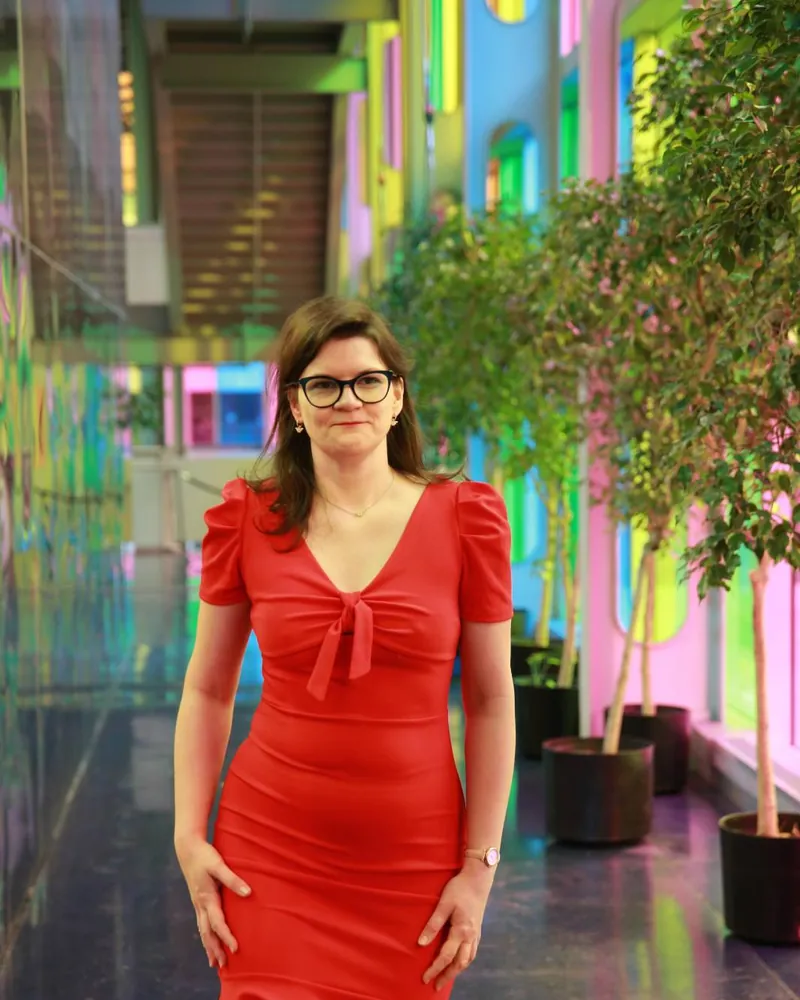
Dorota Kozlowska, known in the community as the Woman in Red, is an offensive security specialist, penetration tester, keynote speaker and podcaster. She is certified in Covert Access, Physical Auditing and Elicitation, and specializes in social engineering and physical penetration testing.
Dorota's path into security began in software quality assurance, where she learned to look at systems from the angle of "how can this break?". That mindset led her into penetration testing and, from there, into the field where technology meets human psychology: social engineering, covert access and red teaming. She has since tested organizations in many countries and openly shares her journey to encourage others making the jump into cybersecurity.
She speaks regularly at international security conferences, including Wild West Hackin' Fest, Disobey, NorthSec, Forum InCyber and BSides events across Europe, hosts the Twitch podcast "Ethical Hacking, Guests, and Wholesomeness", and runs the Woman in Red Community on Discord, home of the Red Talks meetup for first-time and experienced speakers. More about her talks
Recognition
- Cyber Woman of Hope Europe 2023 award, CEFCYS (Le Cercle des Femmes de la CYberSécurité)
- 40 Under 40 in Cybersecurity 2023, Top Cyber News Magazine, including a cover feature
- Honorary Level 99 Top Cyber Pro Award, TopCyberPro.com
Certifications
Publications & Media
- Articles in HVCK and Top Cyber News Magazine
- Preface to Introduction to Red Operations 2.0 by Joas A. Santos
- Technical reviewer of Hacking Mainframes by Kevin Milne
- "My Learning Path to Becoming a Penetration Tester" and "Making a Jump into Penetration Testing from a Non-Cyber Job", CSNP
- Guest on podcasts and shows including Breaking Into Cybersecurity, Cyber Pro Podcast, ITProTV's Ladies in Tech and Outpost Gray's The Female Voice of Technology and Innovation
Languages
Engagements, training and talks are delivered in English and Polish, with working knowledge of German.